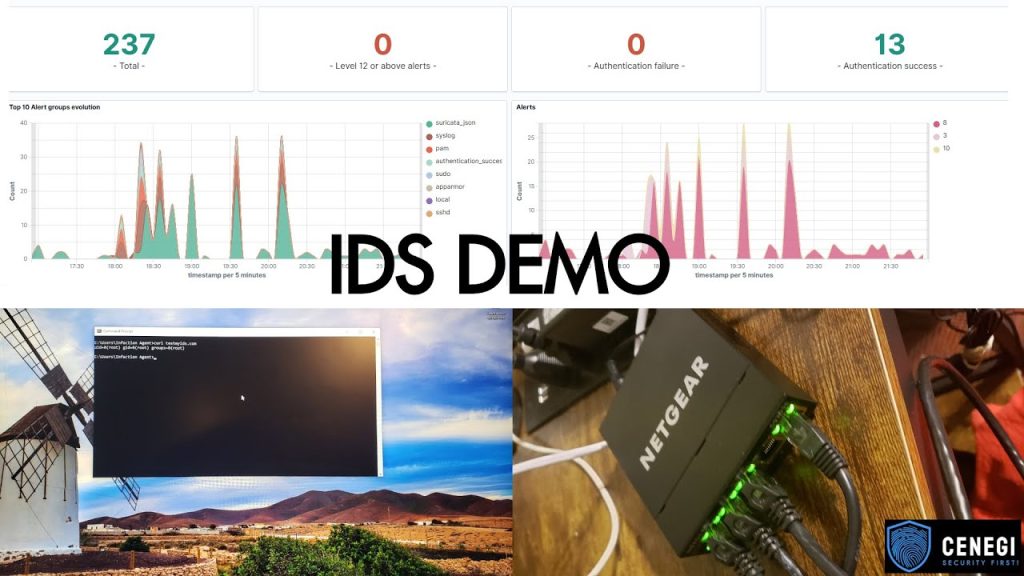
We’ve finished building our Cenegi IDS using Wazuh + a lightweight network sensor to give small businesses real-time visibility into risky activity—without enterprise pricing or complexity. A short demo video is linked at the end.
High-level architecture
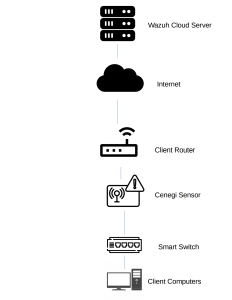
Simple flow of telemetry from your site to Cenegi’s Wazuh cloud for monitoring.
What this actually catches
-
Suspicious or impossible logins (wrong geo/device, brute-force attempts)
-
Hidden inbox forwarding rules and risky mail activity
-
Malware beacons / command-and-control traffic
-
New/unauthorized admin accounts or privilege changes
-
DNS anomalies and other network indicators of compromise
We start with a strong baseline ruleset, then tune detections to your environment to cut noise and surface what matters.
How it works (4 steps)
-
Place a Cenegi Sensor at your site (law firm, manufacturing shop, office).
-
Install lightweight agents (including Wazuh) on key systems to send security events.
-
Securely stream endpoint + network data through an encrypted tunnel to Cenegi’s Wazuh server for ongoing monitoring.
-
Act fast: We review alerts daily, notify you of active threats, and deliver a clear fix plan with recommendations.
What you’ll see in the dashboard
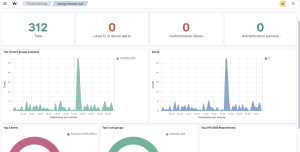
Plain-English alerts, trends, and MITRE-mapped detections.
Why clients like this approach
-
Clarity: Plain-English alerts and weekly summaries—no jargon.
-
Coverage: Endpoint + network + email behaviors in one view.
-
Right-sized: Enterprise-grade visibility, small-business budget.
-
Month-to-month: Prove value first, then scale.
See it in action (short video)
➡️ Watch the Cenegi IDS Demo: IDS Demo Video
Want a quick read on your exposure?
We’ll run a free 15-minute exposure check and send a one-page action plan.
Contact us: Contact Page